How to Audit Your Browser Extensions for Secret AI Data Scraping
Most people can't name what half their browser extensions actually do. This is the audit that tells you which ones are reading everything you type and where that data ends up.
Open your extensions page. You won't recognize half of it.
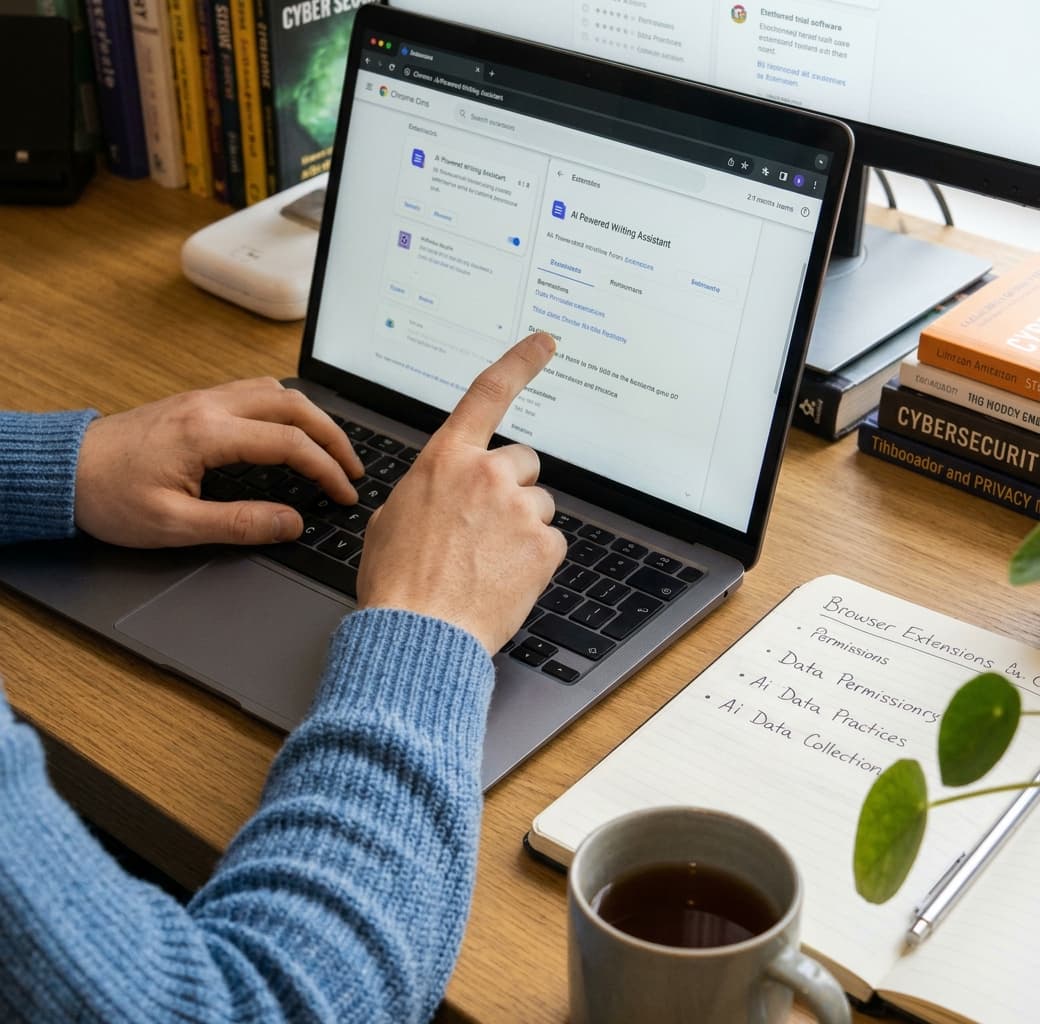
Go to chrome://extensions right now, or about:addons if you're on Firefox. Count what's installed. Most people land somewhere between eight and twenty, and when asked, can explain what maybe three of them actually do. The rest were installed for a PDF conversion in 2022, or a coupon finder someone recommended, or a "productivity" tool that showed up in a YouTube ad.
That gap between what's installed and what's understood is where browser extension security actually breaks down. It's also, increasingly, where a slice of the AI training data pipeline quietly begins — because an extension with broad permissions doesn't just see the page you're reading. It can see the email you're drafting, the chat transcript open in another tab, the internal doc your company just shared with you.
Why browser extension security is suddenly an AI problem
Extensions have always been able to read page content if you grant them access. That's not new. What's changed is the demand side: AI companies and ad-tech firms need enormous, constantly refreshed datasets of real human browsing behavior, and a browser extension is one of the cheapest ways to collect it at scale. Install base, broad permissions, a privacy policy written to be technically accurate and practically unreadable. It's a clean pipeline.
The mechanism is boring, which is exactly why it works. An extension requests "read and change all your data on websites you visit"; you click allow without reading it, and from that point forward it has a legal, disclosed path to log page content, form inputs, and sometimes clipboard activity. Some of that gets bundled and sold as "aggregated browsing insights." Some of it ends up training a model. You usually can't tell which, because the policy language doesn't distinguish.
The DataSpii case is the one worth knowing
In 2019, researcher Sam Jadali documented a case that became known as DataSpii, where a handful of popular browser extensions were caught siphoning full browsing histories — including URLs containing tax documents, internal company dashboards, and private medical records — and selling that data through a marketing analytics firm. Millions of users were affected. The extensions had been in the Chrome Web Store for years, with decent ratings, before anyone traced the leak back to them.
What "permissions" actually mean, in plain terms
The permission list on an extension's details page looks like legal boilerplate, but it's the entire story if you know how to read it. There's a real difference between an extension that can see one site and one that can see everything you do in the browser.
Permission shown | What it actually allows | Risk level |
|---|---|---|
Read and change all your data on all websites | Full access to every page's content, forms, and scripts you load | High — only justified for ad blockers, password managers, grammar tools |
Read your browsing history | A list of every URL you visit, timestamped | High — this alone is enough to build a behavioral profile |
Access to one specific site | Only the domain name, nothing else | Low, if the extension's purpose matches the site |
Storage | Lets the extension save its own settings locally | Negligible on its own |
Clipboard read/write | Can see or alter whatever you've copied | Medium to high, depending on what else it can do |
If an extension's stated purpose doesn't require "all sites" access, and it has it anyway, that's your first flag. A currency converter doesn't need to read your bank's dashboard. A screenshot tool doesn't need your clipboard history going back a week.
The five-minute browser extension security audit
This isn't complicated, and you don't need to be technical to do it. It takes about five minutes per extension the first time, less after that once you know what you're looking for.
Open chrome://extensions (or about: addons on Firefox) and click "Details" on each extension you don't use weekly.
Check "Site access" — if it says "On all sites" for something that has no business reading all sites, that's suspicious on its own.
Click through to the Chrome Web Store or Mozilla listing and read the privacy policy's data section specifically, not the marketing paragraph above it.
Search the extension's name plus "data" or "lawsuit" or "removed" — most scraping scandals get covered by outlets like BleepingComputer or ZDNet within weeks of discovery.
If you can't explain, in one sentence, why this extension needs the access it has, remove it.
Do this for everything, including extensions you trust. Trust isn't static. An extension can be sold to a new owner overnight, and the new owner can push an update that changes what it collects without changing the name or the icon.
The ownership-change trap
This is the part most people miss entirely. In 2021, Google pulled The Great Suspender — a tab-management extension with roughly 2 million users — from the Chrome Web Store after it was sold to an unknown developer and later found to contain code capable of executing remote scripts and tracking user activity. The extension itself hadn't changed its name, its icon, or its description. Only its owner and its behavior.
Spotting a malicious browser extension before it spots you
Malicious browser extension detection isn't about finding obviously broken software. The ones that get caught are usually well-made, well-reviewed, and sitting at four-plus stars right up until a security researcher or journalist flags them. Guardio and other browser-security firms have repeatedly found extension clusters — ad blockers, VPN helpers, screen recorders — quietly injecting scripts that harvest form data and search queries, bundled and sold through third-party data brokers.
The pattern that repeats: a free tool solving a real, small problem, with permissions that go far beyond solving it, backed by a company you've never heard of and can't find much about. That combination is worth treating as a default red flag rather than an edge case.
What to actually do once you've flagged something
Removing an extension doesn't always remove what it already collected. If you find one with broad access that you've had installed for months, assume whatever it could see, it saw. Change passwords for anything sensitive you accessed while it was active, especially financial accounts and anything tied to your identity.
For extensions you genuinely need but don't fully trust, narrow the permission instead of removing it entirely. Chrome and Firefox both let you restrict site access to specific domains rather than "all sites" — most extensions still work fine with this tighter scope, because most of them never needed the broad grant in the first place.
Enterprise environments should go further. If you manage browsers across a team, a managed extension allowlist through Chrome Enterprise or Firefox's policy engine stops this problem before it starts, rather than relying on each person to run their own audit.
The part nobody wants to hear
There's no setting that fixes this permanently. Extension security is maintenance, not a one-time decision, because the extension you vetted in January can be a different piece of software by June. The browser vendors could tighten review processes further, and some of them periodically do a sweep, but the volume of extensions in these stores makes manual review spotty at best.
So the honest answer is that browser extension security mostly comes down to how often you're willing to look. Not glamorous. Still true.
FAQ
How often should I re-run this audit?
Every three months is reasonable for most people, and immediately after any extension pushes a major update. Permission requests can change quietly between versions, which is exactly when a previously trustworthy extension turns risky.
Do star ratings on the Chrome Web Store or Firefox Add-ons tell me anything useful?
Not much. Ratings measure whether an extension works, not whether it behaves. Extensions with 4.7 stars and 2 million users have been caught selling browsing data; the review score reflects the feature, not the backend.
Is Manifest V3 actually safer than V2?
It narrows some background access and limits how extensions can run remote code, which closes a few real loopholes. It does not restrict what a legitimately-installed extension can read from the pages you visit, which is the part that matters for data scraping.
Can antivirus software catch a data-scraping extension?
Rarely, because most of these extensions aren't malware in the technical sense. They do exactly what their permissions allow, which is legal and disclosed somewhere in a privacy policy nobody reads. Antivirus tools look for code that breaks rules, not code that follows them too broadly.
What about extensions on my phone's browser?
Mobile Chrome and Safari don't support traditional extensions, so this specific risk is mostly a desktop problem. The equivalent risk on mobile is app permissions and third-party keyboards, which deserve their own separate audit.